Cloudflare MCP Step-Up Access: Secure AI Agent Guide
Cloudflare has changed a basic security decision for AI agents. On 19 October 2026, it added step-up authorization to the Cloudflare API MCP server. A business can now begin with minimal access and approve an extra permission only when an agent reaches a task that needs it.
That is more than a smoother consent screen. It is a practical way to reduce standing privilege while still letting an agent investigate a problem, prepare a change and request authority at the moment of action.
For Australian small and medium businesses, the useful question is not simply whether to connect an AI agent to Cloudflare. It is how to separate low-risk assistance from changes that can affect DNS, security rules, deployments, data or website availability.
Why this topic is trending now
Cloudflare's release is timely because AI coding and operations agents are moving beyond advice into tool use. Cloudflare says its managed API MCP server covers more than 2,500 API endpoints. That breadth can be useful, but it makes the permission model a business control rather than a minor setup detail.
At the same time, the wider MCP ecosystem is hardening authorization. The 2026-07-28 MCP specification added measures such as authorization-server issuer validation and credential isolation. NIST's current agent identity work is also focused on task-scoped authority, short-lived credentials, revocation and decisions made at the moment an agent invokes a tool.
Cloudflare's step-up flow turns that direction into an immediately usable control: start small, encounter an insufficient_scope challenge, review the requested scope, and decide whether the current task justifies it.
What changed in Cloudflare's MCP access
Previously, teams often faced an uncomfortable choice: grant a broad set of permissions when connecting an agent, or stop the workflow later when a missing permission blocked progress. Step-up authorization creates a third path.
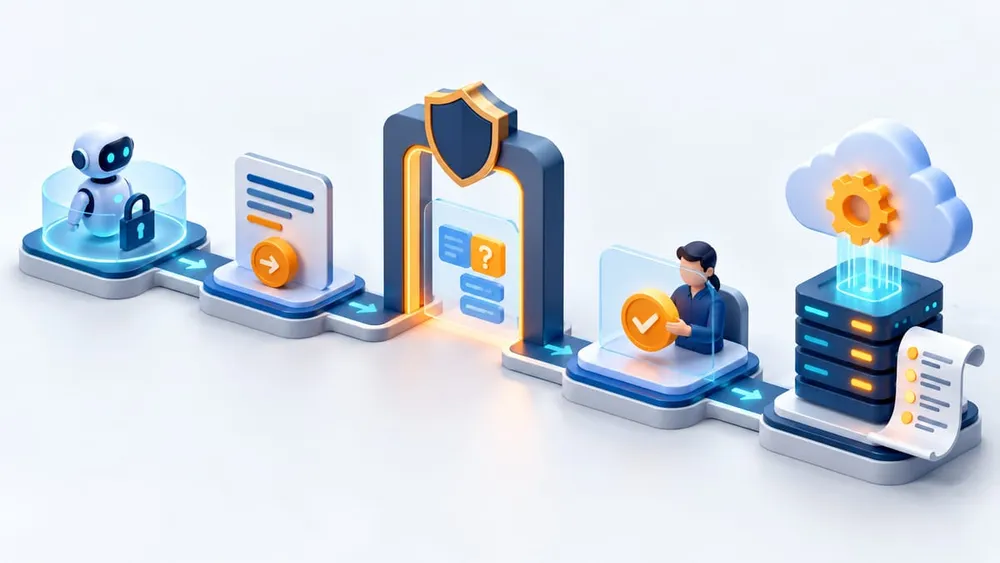
- The user connects the Cloudflare API MCP server and chooses minimal access.
- The agent performs work that fits the scopes already granted.
- A tool call requiring another scope receives an
insufficient_scopechallenge that identifies the missing permission. - A compatible MCP client asks the user to approve that additional scope.
- Existing scopes remain in place and the workflow can continue after approval.
Cloudflare states that this is available in MCP clients that support step-up authorization. Teams should verify their exact client and version rather than assuming every MCP interface will show the same approval experience.
Why it matters to Australian SMEs
Smaller teams often combine website, cloud, security and integration responsibilities. The same person may manage DNS, deploy a Worker, inspect logs and change a firewall rule. A permanently broad token turns one compromised session, mistaken instruction or poorly reviewed tool call into a much larger problem.
The Australian Signals Directorate treats restriction of administrative privileges as an important mitigation because privileged access can change systems, bypass controls and expose sensitive data. The principle applies cleanly to an AI agent acting on behalf of a user: it should not inherit every capability the user might need on another day.
Step-up access can make useful automation easier to approve internally. A business can allow read-only investigation and reporting as a normal workflow, while reserving production changes for a named person, a defined change window and a reviewable request.
Make authority follow the task
Use different controls for different consequences
A useful policy describes the effect of an action, not merely the name of the tool that performs it.
Read and explain
Inspect configuration, logs, analytics or deployment status. Allow by default only where the data sensitivity and tenancy boundary are understood.
Prepare and preview
Draft a rule, calculate a diff or build a deployment plan without applying it. Require evidence, expected impact and a rollback instruction.
Change production
Modify DNS, routes, security controls, deployments or stored data. Require named approval, bounded scope, logging and post-change verification.
Step-up authorization is not the whole security model
Step-up access answers one important question: does this client currently hold the scope required for the tool call? It does not automatically answer whether the user chose the correct account, whether the requested change matches the business intent, whether production is inside an approved change window, or whether the change can be reversed safely.
Cloudflare's Code Mode guidance is explicit that isolated execution does not replace authorization. Permissions and approvals still need to be enforced before side effects. NIST's agent authorization work raises the same broader concerns: task context, delegation, privilege accumulation, revocation, auditability and human-in-the-loop decisions.
Treat the consent prompt as one control inside a chain. The chain should begin with identity and environment selection, continue through intent and risk checks, and finish with execution evidence and review.
Design permissions around business tasks
Avoid creating one broad agent profile called administrator. Start with the workflows the business genuinely wants to improve: investigating a website outage, checking cache behaviour, reviewing security events, preparing a DNS change or deploying an approved Worker version.
| Workflow | Starting authority | Step-up point | Required evidence |
|---|---|---|---|
| Website incident triage | Read logs, analytics and deployment status | Changing configuration or routing | Incident reference, affected service and rollback owner |
| DNS maintenance | Read zones and records | Create, update or delete a record | Proposed diff, TTL impact and validation target |
| Security review | Read rules and events | Enable, disable or alter enforcement | Rule diff, expected match set and false-positive plan |
| Worker deployment | Read project and deployment metadata | Publish or roll back a version | Build result, environment, change owner and smoke tests |
This structure keeps the ordinary investigation path useful while making the high-impact transition visible.
Make the approval prompt worth reading
An approval that only names a technical scope is easy to click without understanding. The surrounding workflow should explain what the agent intends to do, which account and resource are involved, what will change, why the change is needed and how it will be verified.
For higher-risk actions, require a preview or diff before scope elevation. Separate preparation from execution so the agent can assemble the evidence without already holding write access. If the proposed change affects availability, security, customer data or billing, route the approval to a person who owns that consequence.
Approval should also expire as a business decision. Cloudflare notes that previously granted scopes are retained, so teams need a separate process to review and revoke permissions that are no longer justified. Do not confuse on-demand granting with automatic removal.
Keep identity, environments and ownership clear
Use attributable user identities rather than shared administrator accounts. Separate development, staging and production access. Make the active Cloudflare account, zone and environment obvious before an agent presents a change for approval.
If multiple staff members use agents, map scopes to roles and duties. A marketing user who needs analytics should not receive deployment authority. A developer who can prepare a Worker release should not automatically control billing or organisation-wide identity settings.
Cloudflare's authorization guidance supports permission models tied to user roles and MCP tools. Its broader governance guidance separates identity, access conditions and tool scope. Those are useful design boundaries even if a business does not deploy every Cloudflare governance product.
Log both the request and the outcome
A secure workflow needs enough evidence to reconstruct what happened. Record the user, client, time, requested scope, business reason, target account and resource, proposed action, approval decision, execution result and verification result.
Cloudflare's MCP governance documentation describes request and tool-execution logging through Access. Whether a team uses that specific control or another logging layer, the operational goal is the same: distinguish what the agent proposed, what a human authorised and what the API actually changed.
Send high-impact events to a reviewable destination rather than leaving them only in a local agent conversation. Define who checks failed or unusual actions, how long records are retained and how an emergency credential or connection is revoked.
A practical 14-day rollout
Days 1-3: inventory and classify
- List the Cloudflare tasks the team wants an agent to perform.
- Mark each task as read, prepare, reversible change or high-impact change.
- Identify production resources, data sensitivity and current owners.
Days 4-7: connect minimally
- Confirm the chosen MCP client supports step-up authorization.
- Connect with Minimal access and test read-only investigation in a non-production environment.
- Document every scope challenge and check whether the explanation is understandable.
Days 8-11: rehearse controlled changes
- Require a preview, named approver and rollback step before any write.
- Test rejection, expired approval, wrong-environment and partial-failure cases.
- Verify that logs identify the user, requested scope, action and result.
Days 12-14: release one bounded workflow
- Choose a low-frequency, reversible production task.
- Set a review date for retained permissions and the MCP connection.
- Measure time saved, approval quality, failure rate and rollback success before expanding.
Implementation checklist
- Client support: verify the exact MCP client can process Cloudflare's scope challenge and display a usable approval.
- Minimal start: choose Minimal at connection time and document any initial exceptions.
- Resource boundary: make the account, zone, project and environment explicit.
- Task policy: define which actions may run, which may only be prepared and which always need a named approver.
- Preview: require a diff or action summary before write access is requested.
- Rollback: identify the previous state, restore command and responsible person.
- Audit: capture scope requests, decisions, tool executions and verification results.
- Revocation: review retained scopes and disconnect unused clients on a schedule.
If any of these items cannot be answered, keep the workflow read-only until the gap is resolved.
What not to do
- Do not grant broad write access for convenience. A faster first demo is not worth permanent authority across unrelated services.
- Do not treat every scope prompt as safe. Confirm the task, target resource, effect and approver before accepting.
- Do not test destructive actions in production. Use a sandbox or staging account and rehearse rollback.
- Do not rely on the chat transcript as the audit log. Keep durable records connected to identities and API outcomes.
- Do not leave old access in place. Review retained scopes, clients and authorised users after the pilot.
The objective is controlled delegation: enough authority to complete a defined task, for the right person and environment, with evidence before and after the change.
Questions business and technology teams are asking
Sources checked
- Cloudflare: API MCP server step-up authorization release
- Cloudflare: MCP authorization
- Cloudflare: Code Mode MCP server patterns
- Cloudflare: MCP governance
- Cloudflare: Docs for agents
- Model Context Protocol: 2026-07-28 specification release
- NIST: Least privilege
- NIST NCCoE: Agentic AI identity and authorization comments
- Australian Signals Directorate: Restricting Administrative Privileges
Sources were accessed on 20 October 2026. MCP clients and Cloudflare capabilities continue to change, so confirm current compatibility and scope behaviour before implementation.